Running production sites
Websites, SaaS platforms and the servers under them, for clients in the US and UK.
I find the gaps before attackers do, fix them, and explain everything in plain English. Security reviews, hardening and hacked-site recovery for WordPress, WooCommerce, Laravel and the Linux servers they run on. I'm Khurram Shahzad, a technical lead who has run production sites and servers for 8+ years and recovered 50+ attacked websites, so the advice comes from cleanup work, not theory.
Websites, SaaS platforms and the servers under them, for clients in the US and UK.
Cleaned up, entry point closed, hardened and back online.
Managed end to end, without provider-managed hosting add-ons.
Every project is scoped and quoted within 24 hours. No surprises, no long contracts.
A full check of your website, plugins, server, logins and checkout, done by hand, not just a scanner. Included: CMS, plugin and theme audit, user and access review, server and SSL configuration, backup check, checkout and third-party script review, and a known-vulnerability check against current alerts. You get a plain-English report with every issue ranked by risk and exactly how to fix it. Typically 3 to 5 business days.
I fix what the review found, or clean up a site that has already been hacked. Included: malware cleanup, closing the entry point, updates and hardening, firewall setup, credential rotation and a Google Search Console review request when needed. You get a clean, hardened site and a short report of everything changed. Hardening takes days; for a hacked site I start with containment the same day where possible.
Security isn't a one-time job, so I keep watch for you. Included: monthly updates and patching, uptime and change monitoring, tested offsite backups and alerts when a new threat affects your stack. You get a short monthly report: what was updated, what was blocked and anything that needs a decision. Monthly, cancel anytime.
Some sites need help today, others before something goes wrong. Pick the one that sounds familiar.
An active hack needs containment first: take the site offline or block the attack, then clean up and close the way in.
Visitors land on other sites, or Google shows pages you never wrote.
A red warning screen, a 'This site may be hacked' label or a security issue in Search Console.
Admin users, plugins or files you didn't add, or a host that suspended the account.
Most attacks are automated and look for the same weak spots. A review finds yours before a bot does.
A store or booking site where a skimmed checkout costs sales and trust in the same hour.
Plugins, PHP and the server get patched 'when someone remembers'.
An agency client, insurer or partner wants proof that the site is secure.
Tell me what you run and what's worrying you. I'll tell you honestly whether you need me.
I check your site and server by hand and rank every issue by risk, with evidence for each one.
You choose: I apply the fixes, or your team does, using my step-by-step notes.
A plain-English summary of what changed, what's protected now and what to keep an eye on.
Every server in the results below is managed by me end to end: setup, hardening, patching, backups and incident response, with no managed-hosting add-ons from the provider.
An automated scan lists hundreds of warnings without saying which ones matter, and the site stays exposed while the list waits.
I check the site and the server myself and rank every issue by how likely it is to be used against you, so the first fixes are the ones that matter.
I also lead technical SEO, so firewall rules, redirects, caching and cleanups are done without breaking crawling, speed or search visibility.
Every server below is managed by me end to end, shown with each client's permission.
A digital agency hosting 200+ client accounts across 6+ dedicated and VPS servers, with no outside managed-hosting support. I built the servers with WHM/cPanel, gave each client site its own account, put sites behind Cloudflare and ran the security routine: patching, hardened SSL and mail, access control and backups. When attacks got through, I recovered the sites: cleanup, entry point closed, hardened and back online.
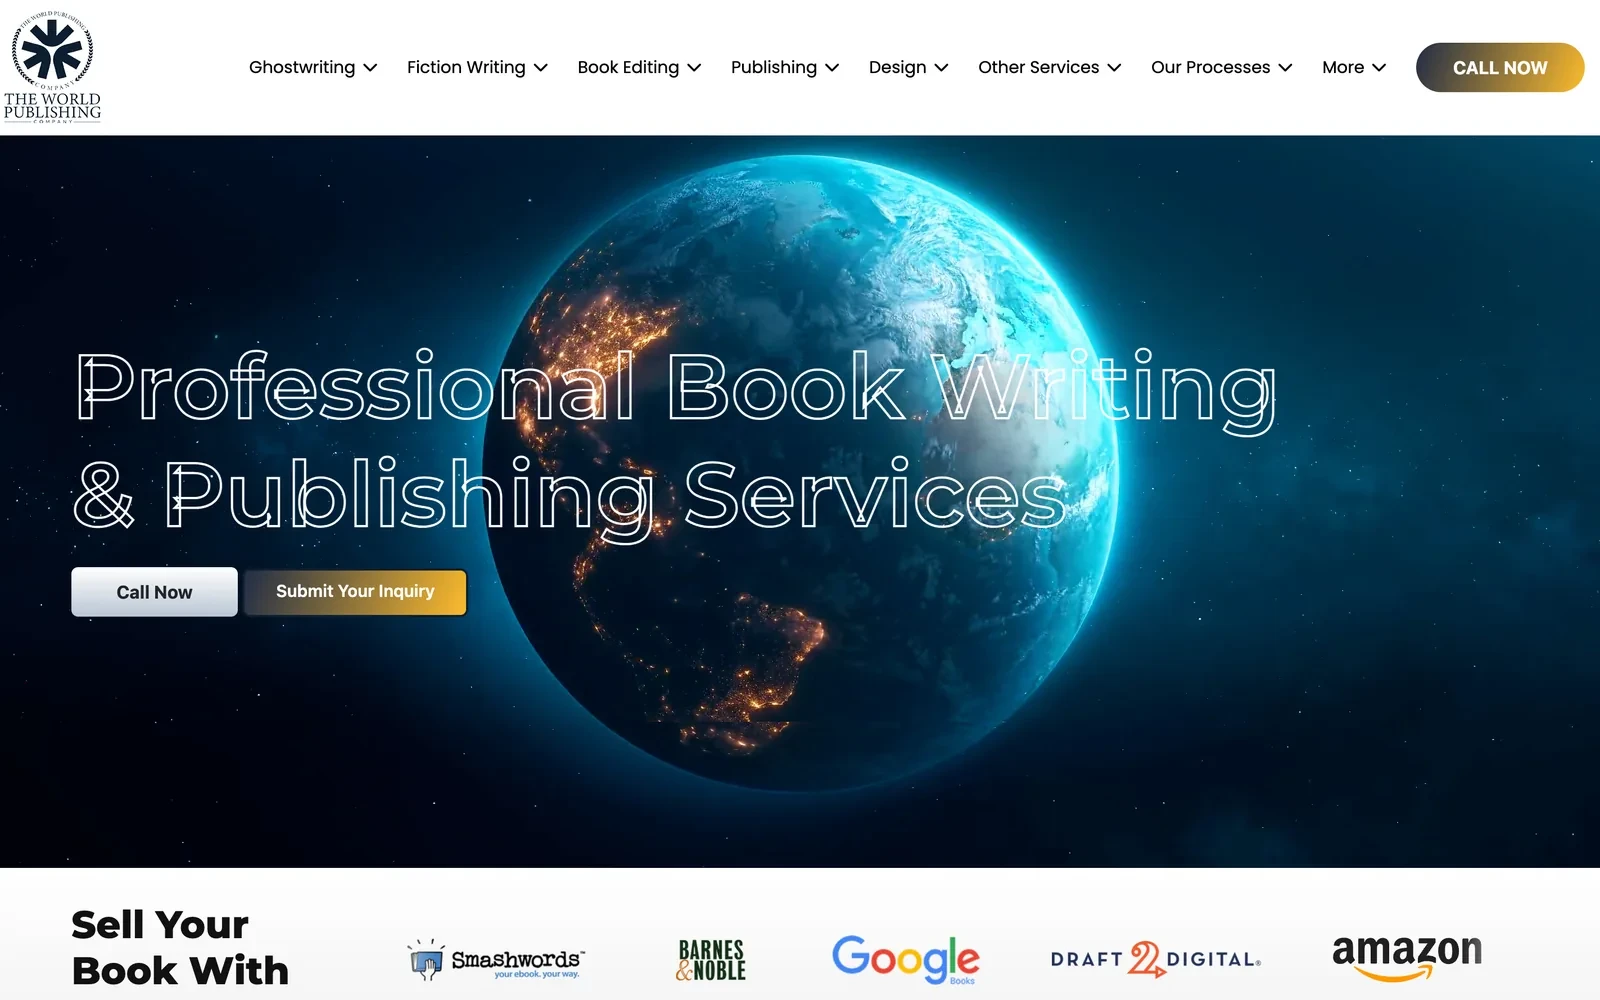
A US publishing business that relies on its website for leads and rankings. I set up and run its dedicated WHM server with Cloudflare in front and security best practices for SSL, access, updates and backups. I also handle the site's SEO, so security and performance changes never hurt rankings. The server has held 99.9% uptime, and organic clicks rose 75% in three months.
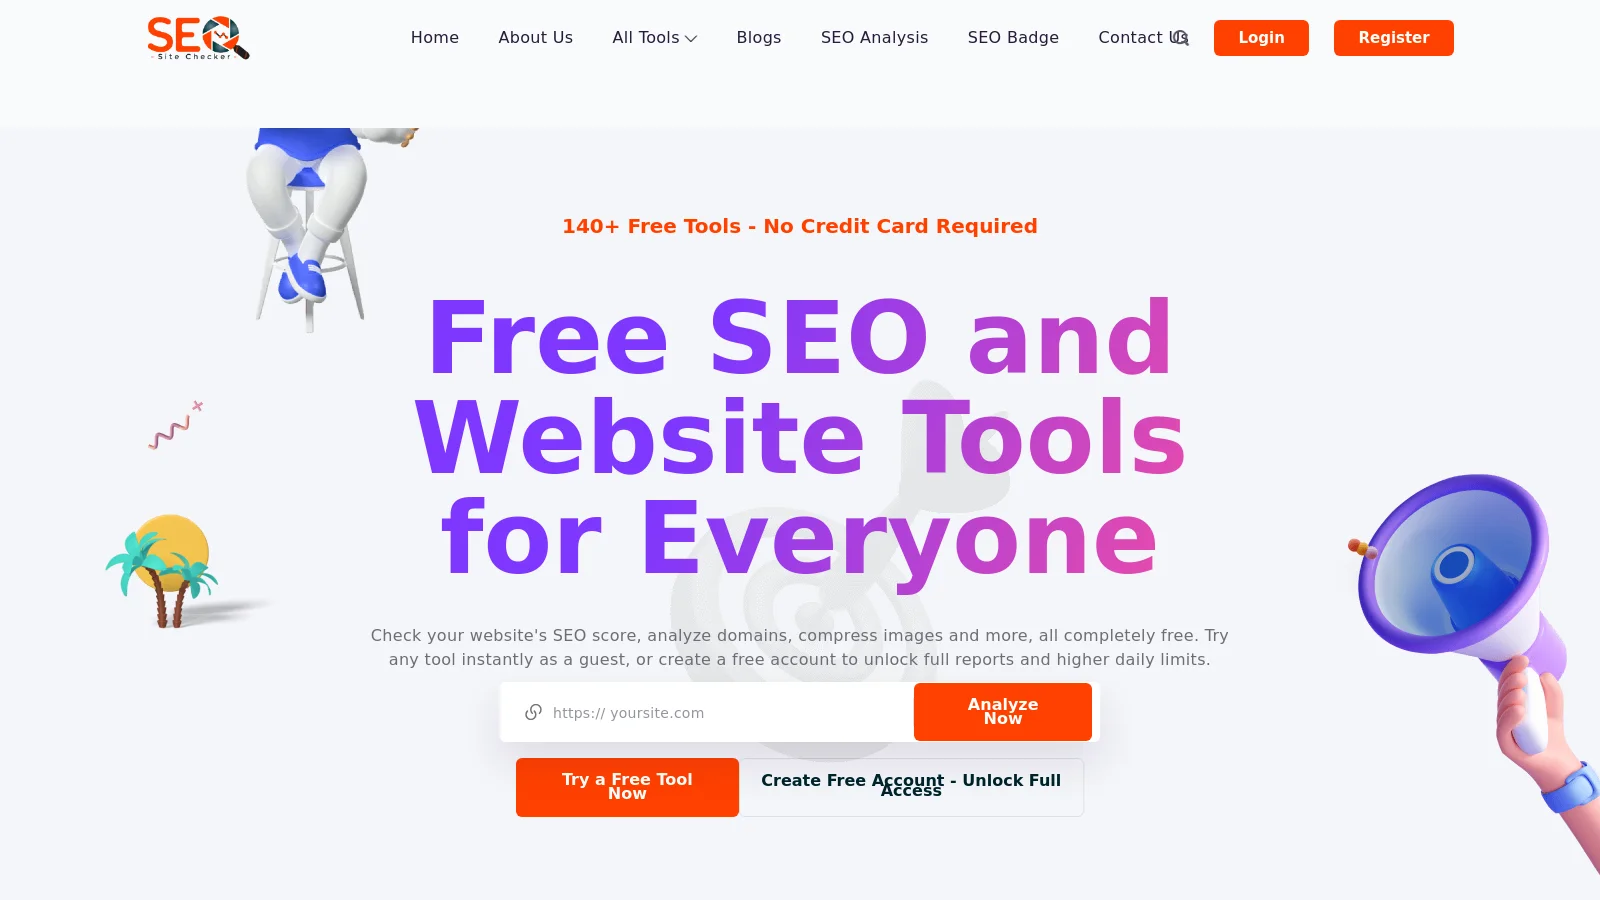
A public SEO tools platform with AI features, on a bare-metal server I run with NexiPanel (CyberPanel-based) behind Cloudflare. I hardened the Dovecot mail server's SSL, fixed a recurring iptables reset that broke Laravel's outgoing email and automated SSL for domain aliases with acme.sh. The stack runs at 99.9% uptime. The platform ranks on page one of Bing for 988 searches.
The right fix depends on the platform, so I work inside the one your site runs on.
Most WordPress hacks start in a plugin or theme, so that is where I look first.
Outdated, abandoned and unused extensions found and removed or updated.
Admin accounts reviewed, 2FA on, file editor off, least privilege.
Payment pages and third-party scripts reviewed for skimming.
I build Laravel apps myself, so I review configuration, secrets and dependencies the way a developer would.
.env files, debug mode, keys and storage permissions checked.
Composer packages and PHP versions patched against known flaws.
Outgoing mail, queues and scheduled jobs that keep working after hardening.
WHM/cPanel, CyberPanel and Docker hosts I set up, harden and patch myself.
Key-only SSH, persistent firewall rules and only the ports you need.
Auto-renewing certificates and hardened mail server SSL.
OS, PHP and OpenSSH kept current, with tested offsite backups.
Shopify runs the server, so the risk sits in apps, staff accounts and checkout scripts.
Installed apps checked for what they can access and whether you still need them.
Staff and collaborator accounts reviewed, 2FA on.
Scripts on checkout and thank-you pages accounted for.
I work best with businesses whose website matters to revenue or reputation, and with teams that need a security specialist without hiring one full time.
If your checkout goes down or gets skimmed, you lose sales and trust in the same hour. I protect the pages that make you money.
You build great sites. When a client gets hacked or asks for an audit, I work under your brand or alongside your team.
You're on Laravel, a VPS or Docker, and security is one of twenty jobs on your list. I give you a clear, prioritized plan and handle the hard parts.
Say 'urgent' in your message. I start with containment, then clean up and close the entry point.
I publish security alerts as threats appear, so the advice you get is current, not a checklist from 2019.
The complete 2026 guide: a self-check, six layers, a 30-day plan and typical costs.
The 8th exploited Chrome zero-day of 2026 and how to patch every browser.
How a long password unlocked key-only accounts on Alpine Linux servers.
How approved commands saved secrets into files that ended up on GitHub.
25 steps to lock down WordPress, including what to do if you're hacked.
The most common web application security risks I check against.
8+ years building and running production websites, SaaS platforms and servers for clients in the US and UK, including 50+ attacked websites recovered.
A verified skills test.
A verified skills test.
Certificate of completion, 21 hours.
Verified skills tests, cloud and DevOps, AI tools and web development, including PHP for WordPress.
Tell me what you run and what's going on. Every project is scoped and quoted within 24 hours, so you know what you're paying for before any work starts. I reply within 1 business day. Available for select consulting projects and full-time roles.
A hands-on check of your site, plugins, server, logins, backups and checkout, with a plain-English report ranked by risk.
I apply the fixes, or clean up a hacked site: malware removed, entry point closed, credentials rotated and the site hardened.
Monthly updates, monitoring, tested backups and threat alerts, with a short monthly report. Cancel anytime.
Often, yes. For an active hack, I start with containment, such as taking the site offline or blocking the attack, then clean up and close the entry point. Get in touch and say "urgent" in the message.
No. I ask for a temporary admin account, SFTP or SSH access just for the project, which you can remove the moment we finish. Never send passwords by email or chat.
It depends on the platform, the number of sites and servers, and whether you want a review only, fixes or monthly care. Every project is scoped and quoted within 24 hours, before any work starts.
Yes. I work with managed WordPress hosts, cPanel hosting, VPS providers and Cloudflare. If your host needs to make a change, I'll tell you exactly what to ask for.
Yes, happily. Client details stay private, and case studies are only published with permission.
Warning signs include unknown admin users, unexpected redirects, spam pages in Google results, browser or Search Console security warnings, new files you didn't add and customers reporting strange checkout behavior. My free website security guide lists the first steps to take.
You get the report and a fix plan. You can have me apply the fixes, hand them to your own team, or move to monthly care. There's no obligation.