A severe security vulnerability was disclosed in React Server Components (RSC) and has been assigned the identifier CVE-2025-55182. This flaw is classified as a CVSS 10.0 critical Remote Code Execution (RCE) vulnerability, meaning an unauthenticated attacker can execute arbitrary code on affected servers.
Because modern frameworks including Next.js, React Router, Waku, Vite RSC, Parcel RSC, and others. Rely on React's Server Components and Server Functions architecture, millions of production applications are impacted.
Frameworks like Next.js 15 and 16, which integrate deeply with Server Components for routing, rendering, streaming, and data handling, are significantly exposed. The Next.js team has published patched releases, with its own CVE tracking identifier (CVE-2025-66478).
This article provides the most complete breakdown available, combining official disclosures with practical developer guidance. You'll learn what caused the vulnerability, exactly which packages and versions are affected, how RCE is achieved, and the specific steps required to update.
Introduction
On December 3, 2025, the React Team published a critical advisory confirming a major flaw in React Server Components and Server Functions. The vulnerability, first reported on November 29, allows an attacker to craft a malicious HTTP request that results in remote code execution on any server using the affected RSC decoding logic.
Key points from the official disclosure:
- Attackers do not need authentication
- The impact is remote code execution (RCE)
- The vulnerability lies in how React decodes payloads sent to Server Function endpoints
- Frameworks using RSC are automatically affected
- Hosting providers deployed mitigations but you must update immediately
This vulnerability is extremely dangerous because RSC packages sit at the core of server-side rendering logic. Even apps that do not explicitly use Server Functions may still be affected if RSC is enabled by the framework.
What is CVE-2025-55182?
CVE-2025-55182 is a flaw in the serialization and deserialization mechanism that React uses to decode payloads in React Server Functions, which are used internally by React Server Components.
How the exploit works:
- The attacker sends a crafted HTTP request to an RSC endpoint or Server Function endpoint.
- React attempts to deserialize the malicious payload.
- Due to improper validation, React decodes data that results in:
- Arbitrary function invocation
- Execution of unexpected code paths
- Direct RCE on the server
Because the vulnerability affects the lower-level RSC packages, any framework or bundler built on them automatically inherits the vulnerability.
This is a maximum-severity issue (CVSS 10.0) because:
- No authentication is needed
- Attack is remote
- RCE is possible
- Exploit can be triggered via crafted network requests
- Many frameworks enable RSC by default
Even if your app does not manually use Server Functions, the decoding mechanism may still be reachable depending on the framework.
Affected Packages
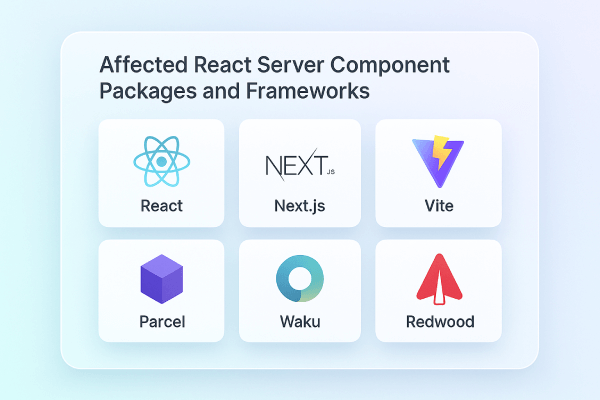 The React team confirmed the vulnerability exists in these RSC packages:
Affected RSC Packages
Affected Versions
- 19.0.0
- 19.1.0
- 19.1.1
- 19.2.0
If your project uses any version of these packages within this range directly or indirectly, you must update immediately.
Affected Frameworks & Bundlers
React confirmed multiple frameworks and bundlers rely on the vulnerable RSC packages:
Affected Frameworks
✔ Next.js
✔ React Router (unstable RSC APIs)
✔ Waku
✔ Expo (when using RSC)
✔ Redwood SDK (with RSC)
Affected Bundlers / Plugins
✔ @parcel/rsc
✔ @vitejs/plugin-rsc
✔ react-server-dom-webpack
✔ react-server-dom-parcel
✔ react-server-dom-turbopack
This means the vulnerability is widespread across the React ecosystem, not limited to Next.js.
Impact on Next.js
Next.js uses React Server Components extensively, especially inside the App Router. This includes:
- Layouts
- Nested routes
- Streaming server rendering
- Server Actions
- Data fetching handlers
Because the RSC architecture is deeply embedded into the Next.js runtime, the vulnerability results in a high chance of exposure.
Next.js-specific risks include:
- Exploitable Server Function endpoints
- RCE via streaming requests
- Unauthorized execution inside the rendering pipeline
- Manipulation of server-side logic
- Risk to environment variables
- Exposure of private server-only data
Vulnerable Next.js Versions (Confirmed)
All versions:
- 15.0.x → 15.5.x
- 16.0.0 → 16.0.6
These correspond to various lines of Next.js's App Router development.
Why This Vulnerability Is So Dangerous (Technical Breakdown)
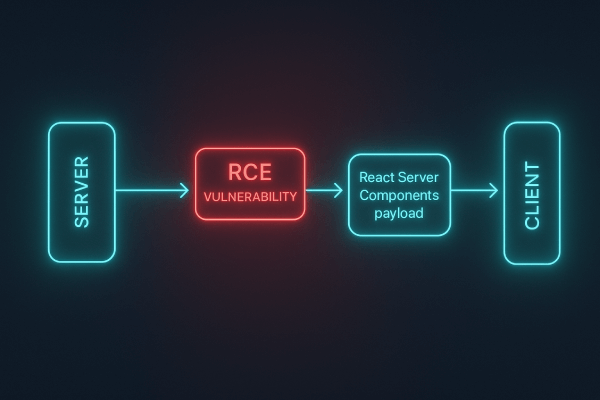
React Server Components rely on a two-way communication pipeline between:
- The client
- The server
- The underlying RSC payload stream
- The Server Function decoder
The vulnerability exists where:
📍 React decodes the payload into executable function calls.
An attacker can craft a malicious payload to cause React to:
- Invoke arbitrary server functions
- Execute unexpected logic paths
- Access privileged data
- Run arbitrary code
This is the definition of Remote Code Execution.
Because RSC is part of the internal rendering process, even apps that do not expose “Server Functions” explicitly may expose endpoints unintentionally via:
- Framework defaults
- Build output
- Bundler tooling
- RSC metadata
This explains why the CVSS score is 10 out of 10.
Severity & Real-World Risks
The vulnerability exposes production apps to:
1. Remote Code Execution
An attacker can execute arbitrary commands on your server instance.
2. Data Theft
If your Server Components fetch:
- user data
- tokens
- secrets
- admin content
…these can be exfiltrated.
3. Unauthorized Access
Attackers may bypass authentication by abusing RSC endpoints.
4. Full Takeover of Production Servers
If your app runs on:
- Vercel Serverless Functions
- Node servers
- Edge runtimes
…the attacker can run code in your environment.
5. Exposure of Infrastructure Secrets
Most Next.js apps expose environment variables in Server Components for server-only logic.
Hosting Provider Mitigations
The React team confirmed that major hosting providers (e.g., Vercel, Netlify, Cloudflare) have deployed temporary mitigations, such as:
- Request filtering
- Additional RSC endpoint hardening
- Payload validation
- Rate limiting
However:
“You should NOT depend on these to secure your app. Update immediately.”
Mitigations are temporary. They are not replacements for upgrading.
How to Fix the Vulnerability
React Patched Versions
Upgrade to:
- 19.0.1
- 19.1.2
- 19.2.1
Next.js Patched Versions
Use:
npm install next@15.0.5
npm install next@15.1.9
npm install next@15.2.6
npm install next@15.3.6
npm install next@15.4.8
npm install next@15.5.7
npm install next@16.0.7
Critical: Canary Versions
If you're on:
⚠ Next.js 14.3.0-canary.77 or later
➡ Downgrade to the latest stable 14.x
npm install next@14
See the Next.js changelog for more info.
General Upgrading Steps
1. Update React & Next.js:
npm install react@latest react-dom@latest next@latest
2. Clear build output:
rm -rf .next
3. Rebuild:
npm run build
4. Redeploy
Full Disclosure Timeline
November 29
- Lachlan Davidson reports the vulnerability via Meta's Bug Bounty
- Severity initially suspected to be critical
November 30
- Meta security team confirms RCE
- React team begins coordinating fixes and testing
- Framework maintainers (Next.js, Redwood, Waku, etc.) notified privately
December 1
- Fixes created
- Coordinated rollout testing begins
- Hosting providers begin applying temporary mitigations
December 3
- Fixes published to npm
- Public disclosure
- CVE-2025-55182 officially published
Should You Delay Deployments?
If your app is running a vulnerable combination of:
- React 19.0-19.2
- Next.js 15-16
- Any RSC package in the affected list
then do NOT deploy or push to production until patched.
If you cannot update immediately:
Temporary mitigations include:
- Restricting access to Server Function endpoints
- Enabling rate limiting or firewalls
- Moving sensitive logic outside Server Components
- Using server-only API routes for critical data
But these only reduce risk.
They do not eliminate it.
Summary & Final Recommendations
CVE-2025-55182 is the most serious vulnerability ever found in React's server-side ecosystem. Because it enables unauthenticated RCE via crafted payloads, and because RSC is widely embedded in frameworks, the potential global impact is enormous.
What you MUST do:
- Upgrade React packages to patched versions
- Upgrade frameworks like Next.js to safe versions
- Downgrade canary releases if applicable
- Rebuild and redeploy your app
- Double-check your package lockfiles
- Continue monitoring React's security feed
Your production environment is not safe until you upgrade.
Frequently Asked Questions
No Tags
Comments (0)